
An AI can help. It cannot go past the locks.
Vantage works with an AI client, and the limits are set by you and by each machine, never by the AI.
Independent, so one mistake is not enough.
- The ceiling. It lives in
/etc/vantage/config.tomlon the machine, owned by whoever owns the machine, and cannot be raised from the dashboard. Insafemode the machine allows restarts and nothing else. This is the answer to the only question a security team really asks: what can this thing do on my server? - Risk tiers. A shell command is priced by what it does rather than by the tool that carries it.
uptimeis one click. A destructive command, such asrm -rf, will not go through until you type the machine's name. The tier check is a seatbelt: a variable or an encoding can get around it. That is why the ceiling sits above it. - The audit. Every call is recorded, including refusals, on the server and in the app, written independently of each other. The audit can be exported as CSV or JSON.
The locks are independent. A command approved by mistake is still refused by a machine in safe mode.
You see it before it happens.
What needs your click
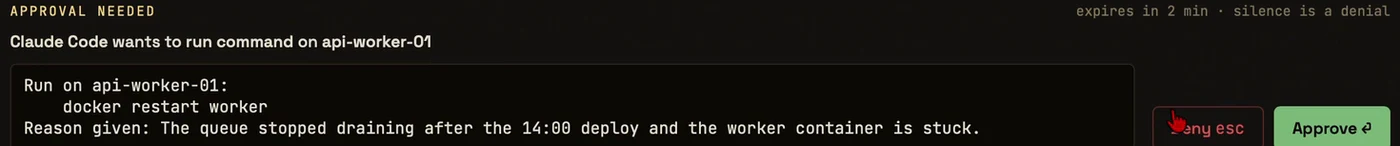
Anything that changes a machine for real waits in an approval you can read: which machine, the exact command and its tier. You decide: Approve or Deny.
The auto-approve window
For debugging a pipeline you can open a window, for one machine if you like. It is scoped, it shuts by itself, it is off unless you choose it, and it never covers a destructive command. An administrator can forbid it on a Mac altogether with a policy file.
Reads need no approval
An AI can read the fleet, logs and metrics, including with the window closed. Logs are capped (at most 1000 lines, 50 series of 500 points per query).
Machine text is data
Text that comes back from a machine is labelled as data, never as instructions, so a log line cannot give your AI orders.
Any MCP client, same rules.
- In Settings, press Add to Claude Code and Vantage runs the command for you. For Claude Desktop, press Add, read the change it shows, then Write it.
- For other clients, copy the JSON or TOML snippet into the client's settings. A client on another machine needs a token: it is shown once, stored hashed and can be revoked.
- Press Test to see the tools the server offers. Calls appear under Activity, with the last call in the monitor.
The same tiers, approvals and audit apply to every client, and an approval says when a request came over the network.
Private by design.
Ask Claude explains an alert in plain words. It is off until you turn it on in Settings, and it has two backends: your own Anthropic API key (kept in the keychain), or Claude Code on your Mac. Claude Code is run with no tools, no MCP servers, no settings and no memory, in an empty temporary folder, so none of yours load.
What is sent
The rule, the reason, the machine label, the site, recent metric numbers and at most a few log lines. The agent has already redacted them and the app scrubs them again: key shapes, PEM blocks, password and token pairs, and JWTs.
What is never sent
Credentials, pins, fingerprints, keys, the MCP token or an invite.
You read it first
Vantage shows the exact text. Send sends exactly those bytes, once per click.
What is kept
The answer is plain text kept only in the window. The audit records the outcome and the byte count, not the content.
The limits that do not move.
It cannot raise a machine's ceiling
The ceiling is a file on the machine. The dashboard, an AI client and an operator cannot change it.
It cannot run a destructive command unattended
A Confirm-tier command needs the typed machine name, and the agent itself refuses it from an operator.
It cannot read your keys or credentials
Credentials, keys and pins are not part of what an AI client or Ask Claude can reach.
It cannot widen the Mac log helper
The helper reads only an allow-list set by the owner with sudo on that Mac, and never runs a command.
It cannot run a playbook behind your back
A destructive playbook step, and every step of an ask-mode playbook, needs your click. No open approval window ever covers a playbook request.
It cannot skip the record
Calls and refusals are audited whether they come from the app, an MCP client or a playbook.
Install Vantage.
Version 1.8.1 for Mac and Linux, signed by AVYR LABS. Free during launch.